




01. Edit your form online
Type text, add images, blackout confidential details, add comments, highlights and more.

Type text, add images, blackout confidential details, add comments, highlights and more.

Draw your signature, type it, upload its image, or use your mobile device as a signature pad.

Send it via email, link, or fax. You can also download it, export it or print it out.
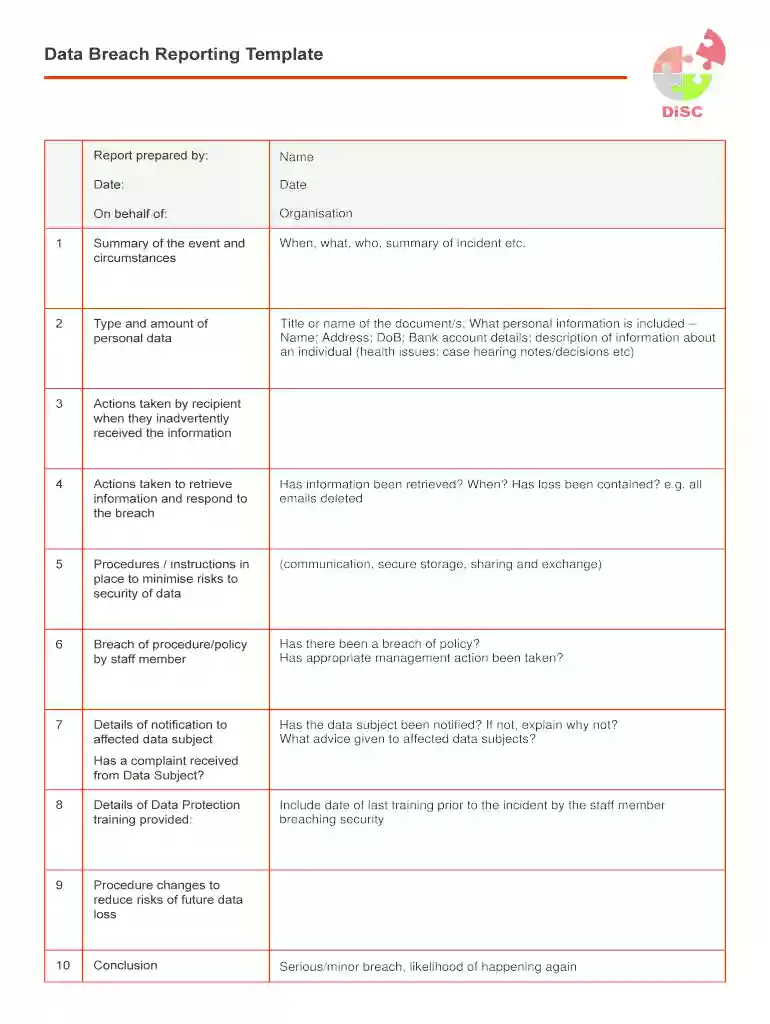
The Data Breach Reporting Template serves as an essential tool for organizations to systematically report incidents involving unauthorized access to personal data. The template is designed to guide organizations through the process of documenting and communicating the key aspects of a data breach. By providing a structured format, the template ensures that all critical information is captured, assisting organizations in complying with legal obligations and maintaining transparency with stakeholders. It emphasizes documenting actions taken in response to the breach, which can be pivotal in mitigating liability and preventing future incidents.
The process of utilizing the Data Breach Reporting Template begins with thoroughly reviewing the sections outlined within the document. Organizations should collect all pertinent details related to the breach, including the nature and scope of the incidents, affected data types, and initial responses. Each section of the template should be completed with accurate and comprehensive information. It is advisable to involve relevant departments and legal counsel in providing input to ensure an accurate representation of events. This collaborative approach ensures all aspects of the breach are addressed, and the report is compliant with regulatory requirements.
The template aligns with U.S. legal standards requiring organizations to report data breaches. Compliance with state-specific laws, such as California's CCPA, is crucial. It ensures organizations meet their legal obligations to notify affected individuals and relevant authorities in a timely and structured manner, minimizing potential legal repercussions.
The template is primarily used by companies across various sectors, including healthcare, finance, and technology. IT security teams, legal departments, and compliance officers are the primary users, leveraging the template to streamline their breach response process and ensure compliance with data protection regulations.
A financial institution that experiences unauthorized access to customer accounts would use the template to document the breach's timeline, affected parties, and remediation steps. Similarly, a healthcare provider discovering a data leak involving patient records would rely on the template to format its response and notification strategies.
Failing to properly report a data breach using the appropriate template can result in significant penalties, including substantial fines and legal action. Non-compliance with reporting obligations can also lead to reputational damage and a loss of consumer trust, emphasizing the importance of adhering to established protocols.
The Data Breach Reporting Template can be efficiently managed and enhanced using document management software like DocHub. With DocHub, stakeholders can collaborate on the template in real time, ensure all document modifications are tracked, and integrate the document seamlessly within Google Workspace, promoting efficiency and accuracy in completing the reporting process.
At DocHub, your data security is our priority. We follow HIPAA, SOC2, GDPR, and other standards, so you can work on your documents with confidence.


The Data Protection Officer should then conduct a full investigation of the data bdocHub and report the findings to the SIRO and other Directors within a.
Use this form to report an unforeseen event, incident, potential, or confirmed bdocHub (incident) to the UW Privacy Office.
You are a New York State government agency or entity reporting a data bdocHub pursuant to New York State Technology Law 208. Your submission will also be sent


