Redo PII in jpeg smoothly


How to Redo PII in Jpeg files anytime from anywhere
Have you ever struggled with modifying your Jpeg document while on the go? Well, DocHub comes with a great solution for that! Access this cloud editor from any internet-connected device. It enables users to Redo PII in Jpeg files quickly and anytime needed.
DocHub will surprise you with what it provides you with. It has robust functionality to make any changes you want to your forms. And its interface is so intuitive that the entire process from start to finish will take you only a few clicks.
Explore DocHub’s features as you Redo PII in Jpeg files:
- Upload your Jpeg from your device, an email attachment, cloud storage, or via a URL.
- Create new content by clicking on our Text tool on the top, and alter its color, size, and fonts as required.
- Click on our Strikeout or Whiteout tools to erase details that just don’t make sense any longer.
- Make visual improvements by drawing or placing images, lines, and icons.
- Highlight crucial details in your paperwork.
- Click on the Comment option to note your most significant modifications.
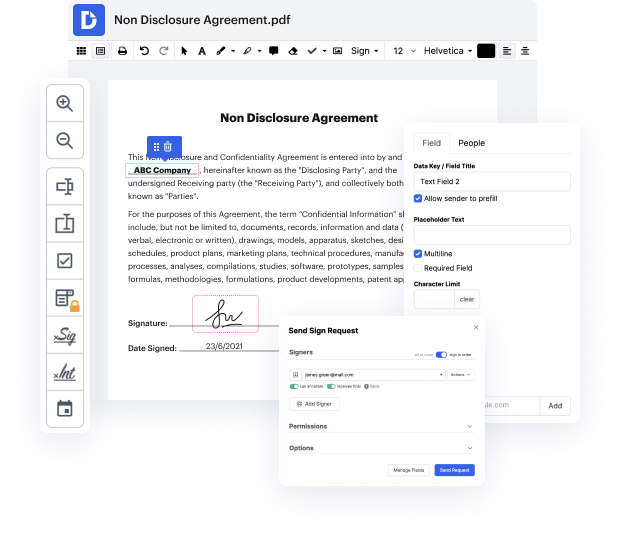
- Transform your Jpeg file into a fillable form by clicking on the Manage Fields tool.
- Place fields for various sorts of data.
- Assign Roles to your fields and set them required or optional to make sure parties fill them out properly.
- Drop Signature Fields and click on Sign to approve your paperwork yourself.
- Select how you share your form - via email or using a shareable link.
When you complete adjusting and sharing, you can save your updated Jpeg document on your device or to the cloud as it is or with an Audit Trail that contains all adjustments applied. Also, you can save your paperwork in its original version or convert it into a multi-use template - accomplish any document management task from anywhere with DocHub. Subscribe today!
PDF editing simplified with DocHub




Drive efficiency with the DocHub add-on for Google Workspace
How to Redo PII in jpeg
foreign photos on your desktop might not be as innocent as you first thought North Korean hacking group apt-37 is hiding malware in digital pictures to evade network detection-based security tools to deliver their malware to devices hey folks this is Ian Garrett in Arlington Virginia on-lab researchers have discovered that apt-37 and North Korean state-sponsored hacking group is using an old vulnerability in the Hangul encapsulated PostScript EPS specifically a type confusion vulnerability in the artifex ghost grip to distribute a new evasive malware called M2 rat the malware is designed to steal personal PC and mobile phone data as well as execute commands and take screenshots its also capable of scanning for portable devices copying data from them and sending a password protected compressed archive to the attacker server there is also an interesting steganography component of this attack which is the practice of concealing information within other non-secret data instead of directly

See why our customers choose DocHub


Security and compliance
At DocHub, your data security is our priority. We follow HIPAA, SOC2, GDPR, and other standards, so you can work on your documents with confidence.
Learn more