



01. Edit your form online
Type text, add images, blackout confidential details, add comments, highlights and more.

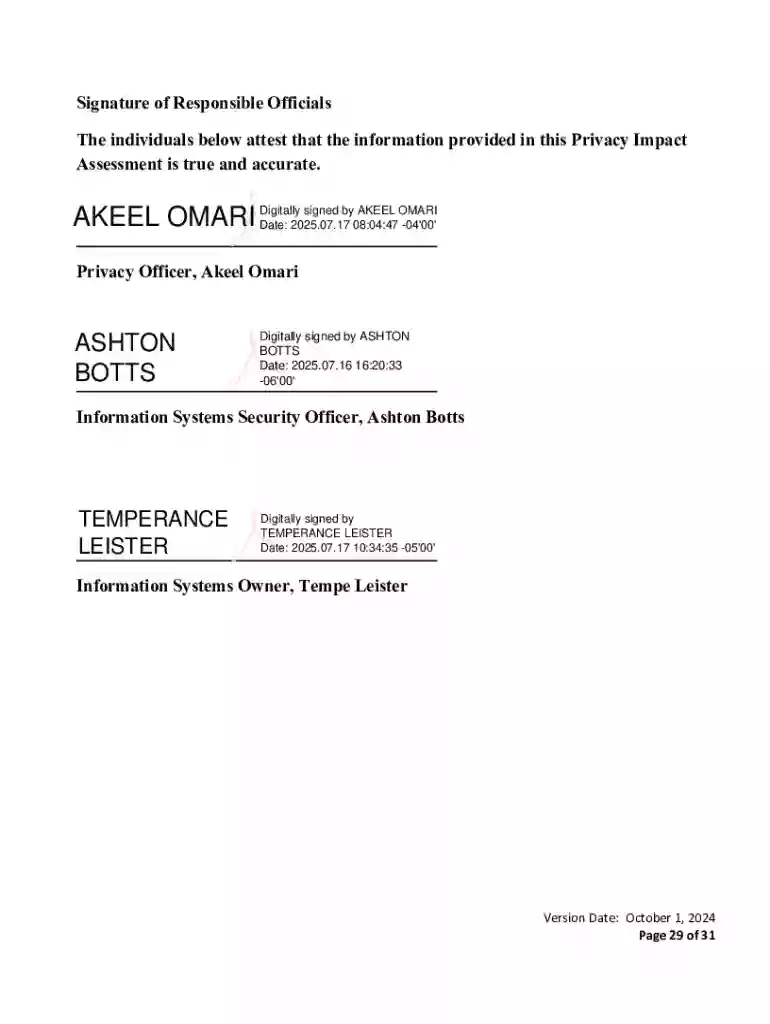
Type text, add images, blackout confidential details, add comments, highlights and more.

Draw your signature, type it, upload its image, or use your mobile device as a signature pad.

Send it via email, link, or fax. You can also download it, export it or print it out.
A Privacy Impact Assessment (PIA) for the VA IT System is a process used to evaluate the potential privacy risks associated with the Veterans Affairs' Information Technology systems. This assessment aims to ensure that veteran data is handled responsibly and protected against unauthorized access. Conducting a PIA helps in identifying potential vulnerabilities in the system and suggests measures to mitigate identified risks. The PIA is particularly vital for systems that process or store Personally Identifiable Information (PII) related to veterans' healthcare and benefits.
The VA IT System's PIA includes several crucial components that facilitate a comprehensive evaluation. These components encompass information collection practices, legal authorities governing data use, privacy risks, and security measures. It's important to note that the system aligns with privacy regulations such as HIPAA to safeguard sensitive information. Other key elements involve detailing the scope of data handling, identification of data flows, and the mechanisms in place for data minimization and retention.
Using the PIA involves several steps to analyze the privacy implications of data handling within the VA IT System. Users must evaluate:
A thorough understanding of the system's architecture and processes will facilitate a more accurate assessment.
Completing a PIA involves a structured approach:
Primarily, those involved in the management and operation of VA IT Systems, including IT professionals, data privacy officers, and compliance managers, use the PIA. These individuals need to understand the privacy implications and ensure data protection measures are in place. Additional users include data analysts and legal advisors who require insights into privacy management as part of their responsibilities.

Performing a PIA is essential for legal compliance and is aligned with several federal regulations, including the Privacy Act and HIPAA. The assessment helps ensure that the VA's IT systems adhere to data protection standards, minimizing the risk of legal penalties. Complying with these regulations is crucial not only for protecting veteran data but also for maintaining the integrity and reputation of the Veterans Affairs operations.
Understanding specific terminology is essential for effectively using the PIA. Key terms include:
Grasping these terms is crucial for anyone involved in data privacy assessments within the VA IT system.
Examples of the PIA in action include its application in evaluating specific IT systems like the Fee Basis Claims Archive (FBCA). For instance, the PIA determined that FBCA is a read-only archive, emphasizing data security by preventing external data sharing. Other scenarios involve assessing new systems to ensure compliance and identifying any necessary improvements to existing systems to enhance data security.
The PIA application process within the VA system involves a series of steps:
The approval time varies based on the complexity of the assessment and the current workload but typically involves a detailed review and revision process to ensure thoroughness.
We've got more versions of the Privacy Impact Assessment for the Va It System form. Select the right Privacy Impact Assessment for the Va It System version from the list and start editing it straight away!
At DocHub, your data security is our priority. We follow HIPAA, SOC2, GDPR, and other standards, so you can work on your documents with confidence.


2 days ago Privacy Impact Assessments are consistently reviewed to ensure they are accurate and up to date. Below is a list of VA Privacy ImpactRead more
Cohesity gives you both data security and data management. A single, secure platform to protect 1,000+ workloads, accelerate recovery, and unlock insights from
A Privacy Impact Assessment (PIA) must also be provided to the COR and approved by VA Privacy Service prior to approval to operate.


