cyber security assessment checklist Preview on Page 1

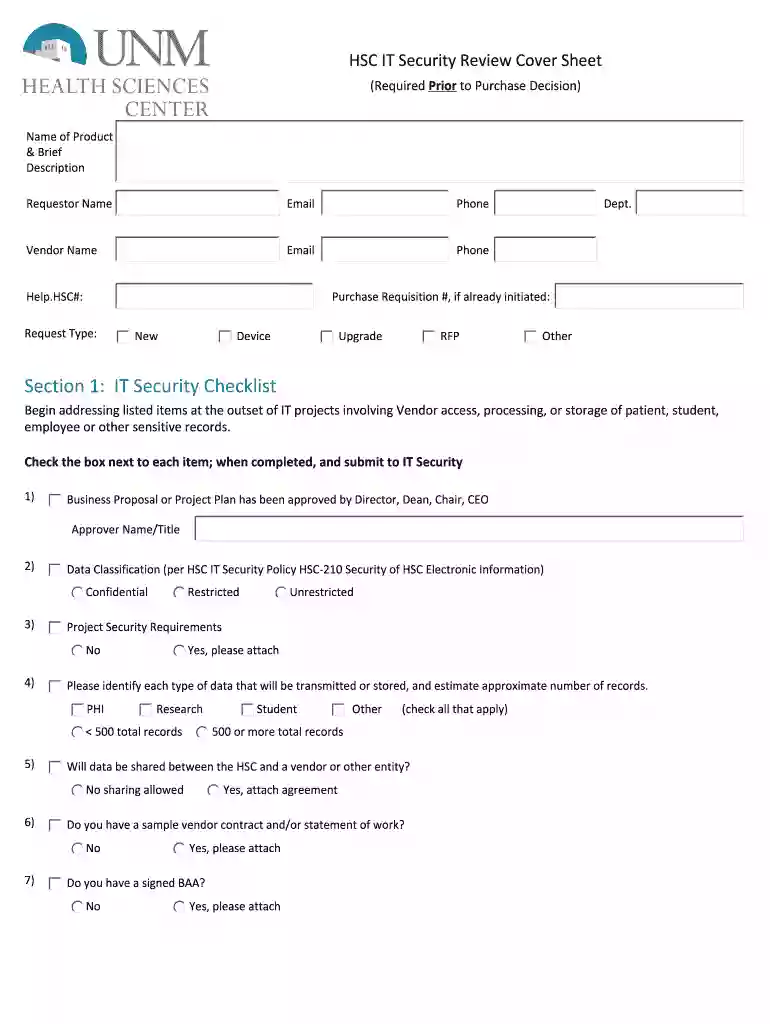
Section 1: IT Security Checklist 2026

Here's how it works

  • 01. Edit your cyber security assessment checklist online

    Type text, add images, blackout confidential details, add comments, highlights and more.
  • 02. Sign it in a few clicks

    Draw your signature, type it, upload its image, or use your mobile device as a signature pad.
  • 03. Share your form with others

    Send cyber security audit checklist via email, link, or fax. You can also download it, export it or print it out.
How to use or fill out Section 1: IT Security Checklist with our platform

Form edit decoration
9.5
Ease of Setup
DocHub User Ratings on G2
9.0
Ease of Use
DocHub User Ratings on G2
  1. Click ‘Get Form’ to open the IT Security Checklist in the editor.
  2. Begin by entering the 'Name of Product & Brief Description' and 'Requestor Name' along with their email and phone number. This information is crucial for identifying the project.
  3. Fill in the 'Vendor Name' and their contact details. Ensure accuracy as this will be used for communication regarding security requirements.
  4. Select the 'Request Type' from options such as New Device, Upgrade, RFP, or Other. This helps categorize your request appropriately.
  5. In Section 1, check each item as you complete it. Start with confirming that a Business Proposal or Project Plan has been approved by the necessary authority.
  6. Classify your data according to HSC IT Security Policy by selecting Confidential, Restricted, or Unrestricted. Provide estimates of records for each type of data being transmitted or stored.
  7. Indicate whether data will be shared with a vendor and attach any necessary agreements. Confirm if you have a signed BAA and attach it if applicable.

Start using our platform today to streamline your document editing and ensure compliance effortlessly!

be ready to get more

Complete this form in 5 minutes or less

Got questions?

We have answers to the most popular questions from our customers. If you can't find an answer to your question, please contact us.

Change, Compliance, Cost, Continuity, and Coverage; these are all fundamental considerations for an organization. For anyone challenged with evaluating and implementing technical solutions, these factors provide a useful lens through which to assess available options.
The National Checklist Program (NCP), defined by the NIST SP 800-70, is the U.S. government repository of publicly available security checklists (or benchmarks) that provide detailed low level guidance on setting the security configuration of operating systems and applications.
You can put the NIST Cybersecurity Framework to work in your business in these five areas: Identify, Protect, Detect, Respond, and Recover.
7 NIST RMF Steps How to Apply Them Step 1: Prepare. The first step of NISTs RMF guidance is to prepare all levels of your organization to manage its security and privacy risks through the RMF. Step 2: Categorize. Step 3: Select. Step 4: Implement. Step 5: Assess. Step 6: Authorize. Step 7: Monitor.
The key components of an IT security policy include confidentiality, integrity, and availability, also known as the CIA triad, and authentication.

Security and compliance

At DocHub, your data security is our priority. We follow HIPAA, SOC2, GDPR, and other standards, so you can work on your documents with confidence.

People also ask

Combined, this makes up our NIST 800-171 compliance checklist. NIST 800-171 was created to help government contractors and subcontractors minimize their cybersecurity risk, protect their networks, and secure controlled unclassified information (CUI).
By using software developed on the four security pillars of monitoring, secure development, testing, and maintaining compliance with cutting- edge federal and international standards, organizations can trust that their data and information will have the strongest protection against potential attacks.
The NIST CSF was designed with the intent that individual businesses and other organisations use an assessment of the business risks they face to guide their use of the framework in a cost-effective way.

cyber security checklist pdf

Information Security Checklist - Office of OneIT - UNC Charlotte

The Information Security Checklist is a starting point to review information security related to the systems and services owned by each unit, department,Read more

Learn more
IT Security Checklist - Washington State Health Care Authority

The IT Security Checklist contains three sections: Section 1 - Agency and System Characteristics Cost: $3,000; Schedule: 1 week; Resources: 1 developer, 1Read more

Learn more
Information Security Checklists (Level 1)

Information Security Checklists (Level 1) Third-Party Service Registration Public Information Posting Authorization Public Website Confidential Info

Learn more
If you believe that this page should be taken down, please follow our DMCA take down process here