01. Edit your form online
Type text, add images, blackout confidential details, add comments, highlights and more.

Type text, add images, blackout confidential details, add comments, highlights and more.

Draw your signature, type it, upload its image, or use your mobile device as a signature pad.

Send it via email, link, or fax. You can also download it, export it or print it out.
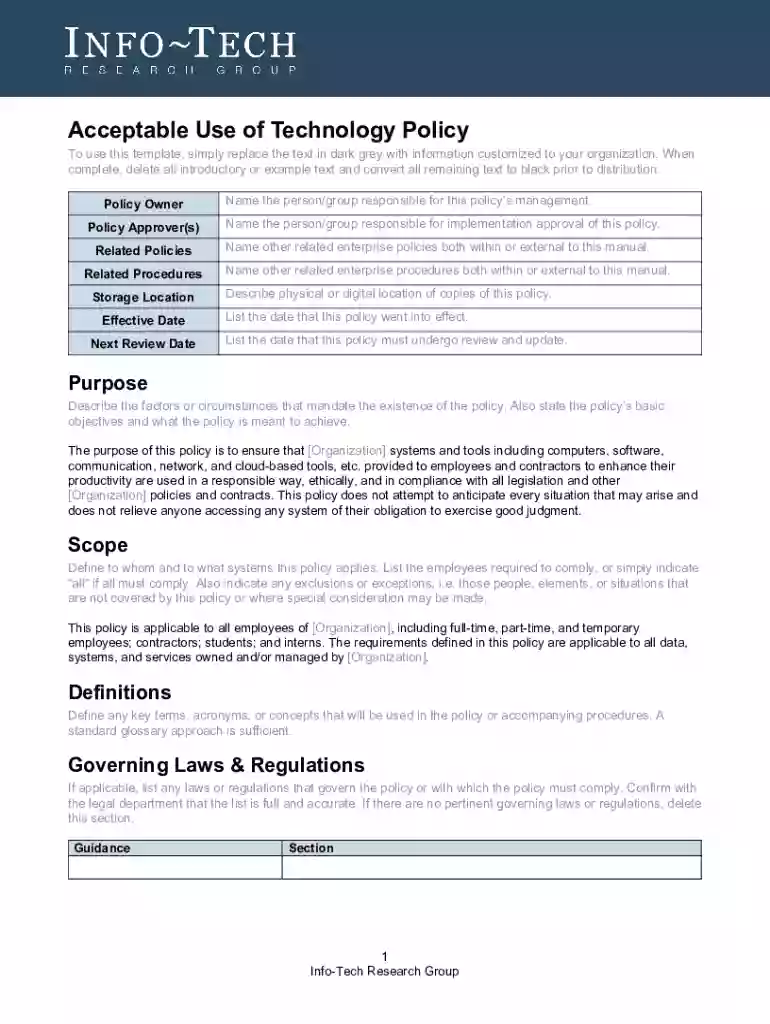
An Acceptable Use Policy (AUP) outlines the standards and expectations for the use of organizational technology resources. It sets the framework within which employees, contractors, and other users interact with technology tools and data. The policy is vital in maintaining a secure and efficient digital environment. At its core, an AUP defines lawful and ethical behaviors expected during the utilization of computers, networks, and electronic communication systems. This document helps safeguard company data and assets, clarifying permissible activities and highlighting potential liabilities and consequences of misuse.
A robust AUP must cover several critical areas to be effective. Components typically include guidelines for acceptable personal use, indicating what types of activities are allowed during working hours on company devices. Data security provisions highlight requirements for data protection, encryption, and unauthorized data access restrictions. Furthermore, directives surrounding mobile device management ensure proper usage and data protection when using smartphones and tablets. The policy encompasses electronic communication protocols that set standards for email usage, data sharing, and digital interactions. Rules regarding social media usage are delineated to maintain professionalism and confidentiality online. Password management directives stress the importance of strong passwords and regular updates. Finally, the policy describes incident reporting procedures to handle potential violations or breaches efficiently.
The template is essential for organizations aiming to enforce proper technology usage rules. It aids in establishing a legal foundation for disciplinary measures when policy violations occur, offering protection for the company against legal disputes resulting from improper use of technology resources. Organizations must align their AUP with applicable laws, including data privacy and cybersecurity regulations. This alignment helps mitigate risks of litigation and ensures compliance with federal and state-level legal requirements in the United States.
Consider a company utilizing the AUP to manage employee behavior regarding internet use in the workplace. Prior to implementing the policy, employees may access inappropriate websites that compromise network security. With the policy enforceable, the company clearly communicates acceptable websites and software, how to report potential security threats, and consequences for disregarding the policy. A second example can include managing remote work settings, where the policy outlines the conditions under which employees can access company data from personal devices to ensure security and integrity.
Organizations across various industries can benefit significantly from adopting an AUP. Technology-based sectors, such as IT services and software development, require stringent policies to protect sensitive information and intellectual property. Similarly, financial services firms that handle confidential client data benefit from enhanced security measures mandated by a well-crafted AUP. Educational institutions also rely on AUPs to govern the use of technology by students and staff, promoting a productive and secure learning environment.
It is crucial that AUPs are adapted to adhere to state-specific regulations in the United States. For example, California businesses must comply with the California Consumer Privacy Act (CCPA), which affects how data is managed and protected. Similarly, organizations in Texas should pay attention to the Texas Business and Commerce Code regarding electronic communications and security measures. Different states may have varying privacy laws, making it necessary to tailor the AUP to address state-specific legal requirements.
Besides a standard template, there are various AUP formats and examples that organizations can consider, depending on their industry and requirements. Some businesses opt for concise summaries focusing exclusively on critical guidelines, while others favor detailed step-by-step instructions to cover every possible technology interaction. Alternatives may include templates integrated with employee handbooks or those emphasizing mobile device usage and cloud-based services. Tailoring the document to meet organizational preferences and technological landscapes is key for an effective policy.
At DocHub, your data security is our priority. We follow HIPAA, SOC2, GDPR, and other standards, so you can work on your documents with confidence.