

Here's how it works
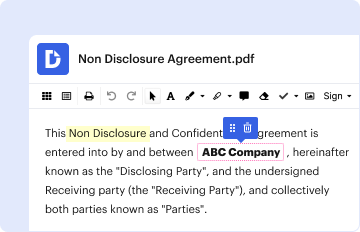
01. Edit your acceptable use policy form online
Type text, add images, blackout confidential details, add comments, highlights and more.
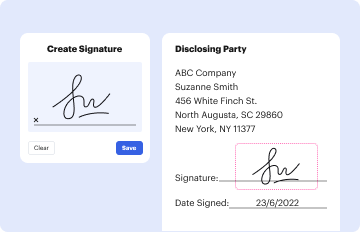
02. Sign it in a few clicks
Draw your signature, type it, upload its image, or use your mobile device as a signature pad.
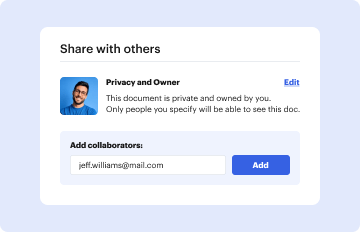
03. Share your form with others
Send dod use policy via email, link, or fax. You can also download it, export it or print it out.
How to use or fill out the acceptable use policy form with our platform
- Click ‘Get Form’ to open the acceptable use policy form in the editor.
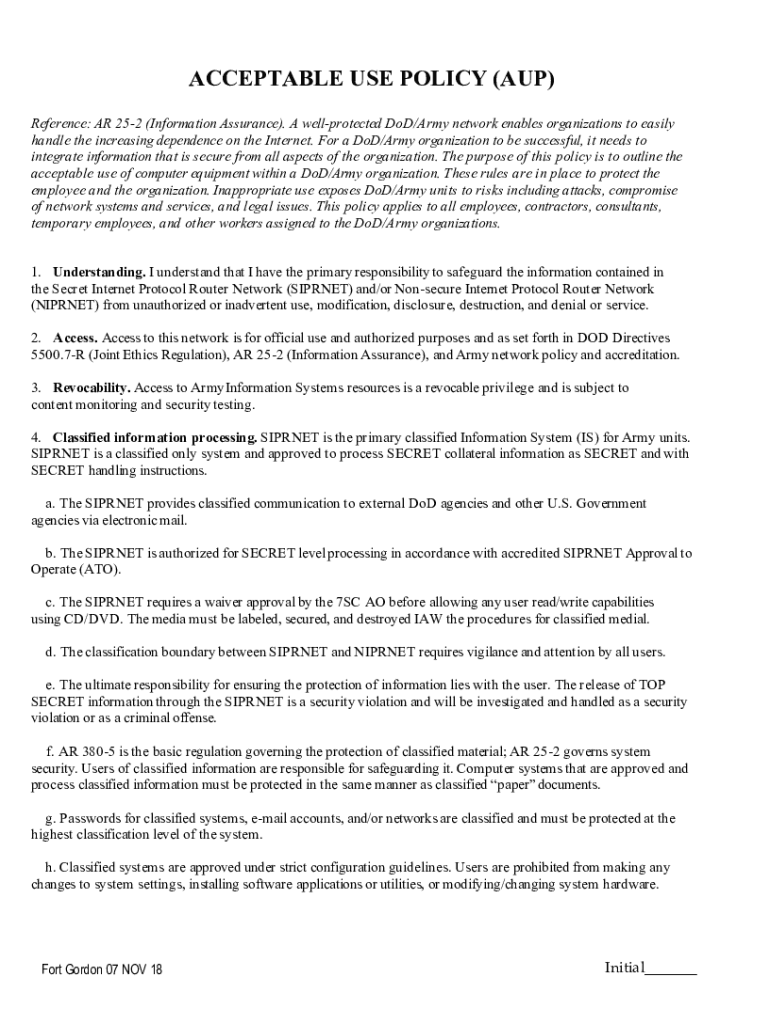
- Begin by reviewing the 'Understanding' section. Acknowledge your responsibility to safeguard information on SIPRNET and NIPRNET by checking the corresponding box.
- Proceed to the 'Access' section. Ensure you understand that access is for official use only, and confirm this by signing in the designated area.
- In the 'Revocability' section, read through the terms regarding access privileges. Confirm your understanding by initialing next to each point.
- Fill out personal details at the end of the document, including your name, rank/grade, and contact information. Make sure all entries are accurate before submitting.
Start using our platform today to easily complete your acceptable use policy form online for free!
Fill out acceptable use policy form online
It's free
It's free
See more acceptable use policy form versions
We've got more versions of the acceptable use policy form form. Select the right acceptable use policy form version from the list and start editing it straight away!
Got questions?
We have answers to the most popular questions from our customers. If you can't find an answer to your question, please contact us.
Contact us
What is an acceptable use policy and give three examples?
An AUP sets rules related to an organizations IT security policies. These include rules around accessing restricted information; changing access data, such as passwords; opening questionable email attachments; accessing public Wi-Fi services; and using company-approved authentication procedures.
What is the difference between an AUP and a TOS?
An AUP is very similar to a Terms of Service or an End-user License Agreement text that can be found on almost all software applications. There are a few differences in the documents, though. AUPs tend to cover a larger range of computer resources, like websites. They also cover etiquette and respect for other users.
What should not be part of an acceptable use policy?
Encryption policies not be part of an acceptable use policy. We should not allow ADVERSITY to discourage us . What is used in most programs that is a part of a program and guides the user through certain steps?
What are the three things included in an acceptable use policy?
An acceptable use policy usually: Includes specific rules, such as no video pirating. Outlines consequences for breaking the rules, such as warnings or suspension of access. Details an organizations philosophy for granting access (for example, internet use is a privilege that can be revoked, rather than a right)
What is the acceptable use policy document?
The purpose of the acceptable use policy is to outline the acceptable use of computer equipment at the company. These rules are in place to protect the authorized user and the company. Inappropriate use exposes the company to risks including virus attacks, compromise of network systems and services, and legal issues.
Security and compliance
At DocHub, your data security is our priority. We follow HIPAA, SOC2, GDPR, and other standards, so you can work on your documents with confidence.
Learn more


People also ask
What is an acceptable use policy for contractors?
An Acceptable Use Policy typically governs the usage of resources like systems, networks, and devices within the organization. The policy must cover all individuals accessing company networks, including employees, contractors, and affiliates, ensuring everyone is held to the same standards.
What is an acceptable use policy document?
An acceptable use policy is a document that service owners use to outline all rules pertaining to service users. If someone breaks those rules, the AUP also outlines the consequences and any actions the service might take in response.