

Here's how it works
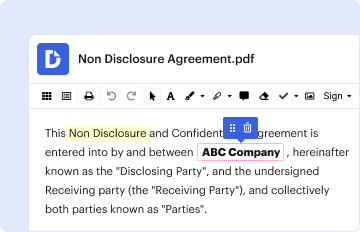
01. Edit your form online
Type text, add images, blackout confidential details, add comments, highlights and more.
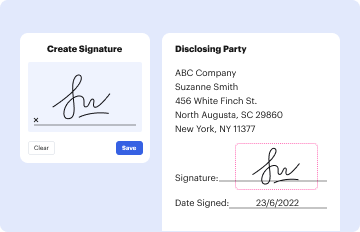
02. Sign it in a few clicks
Draw your signature, type it, upload its image, or use your mobile device as a signature pad.
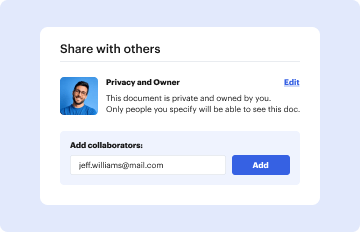
03. Share your form with others
Send it via email, link, or fax. You can also download it, export it or print it out.
How to use or fill out Information Security Incident Reporting and Response Policy with our platform
- Click ‘Get Form’ to open the Information Security Incident Reporting and Response Policy in the editor.
- Begin by reviewing the 'Personnel Roles' section. Fill in your name and role as required, ensuring clarity on your responsibilities during an incident.
- Proceed to the 'Roles During Incident Response' section. Indicate your designated role by selecting from the provided options, which may include Incident Commander or Biological Safety Officer.
- In the 'RLSS Emergency Responders' section, list any emergency responders you will coordinate with. Ensure their contact information is accurate for quick access during incidents.
- Complete the 'Site Security' field by confirming adherence to security protocols outlined in the Biosecurity Plan. This may involve checking off compliance items.
- Review and fill out any additional sections such as 'First Aid', 'Spills of Infectious Material', and others as applicable, following the detailed instructions provided within each section.
Start using our platform today to streamline your document editing and ensure a smooth incident response process!
Fill out Information Security Incident Reporting and Response Policy online
It's free
It's free
See more Information Security Incident Reporting and Response Policy versions
We've got more versions of the Information Security Incident Reporting and Response Policy form. Select the right Information Security Incident Reporting and Response Policy version from the list and start editing it straight away!
Got questions?
We have answers to the most popular questions from our customers. If you can't find an answer to your question, please contact us.
Contact us
What is NIST 800-171 in a nutshell?
The cybersecurity requirements within NIST SP 800-171 are designed to safeguard CUI in the IT networks of government contractors and subcontractors. It defines the practices and procedures that government contractors must adhere to when their networks process or store CUI.
What is incident response and reporting policy?
The Incident Response Policy (IR Policy) provides the structure and activities required to effectively respond to an information security incident and minimize negative impact to the confidentiality, integrity, and availability of institutional data and its information technology (IT) assets.
What is the NIST 800-171 security plan?
A System Security Plan (SSP) is a living, comprehensive document that explains exactly how your organization implements and uses the security controls outlined in SP NIST 800-171 to protect CUI. You can think of it as your blueprint for how your company protects sensitive information.
What are the 6 steps of SANS?
The SANS incident response process includes the following steps: preparation, identification, containment, eradication, recovery, and lessons learned.
What is the NIST incident response 800-171?
Incident response is one of the 14 requirements outlined in the National Institute of Standards and Technologys (NIST) Special Publication (SP) 800-171Protecting Controlled Unclassified Information (CUI) in Nonfederal Information Systems and Organizations and enforced by the U.S. Department of Defense (DoD).
Security and compliance
At DocHub, your data security is our priority. We follow HIPAA, SOC2, GDPR, and other standards, so you can work on your documents with confidence.
Learn more


People also ask
What is incident response plan by NIST?
NIST Incident Response Framework: The 4 Steps. The NIST framework includes four stages: preparation and prevention; detection and analysis; containment, eradication, and recovery; and post-incident activity.
What is the information security incident response policy?
An incident response policy is a document outlining your organizations game plan for how to respond to a cyber security incidents. It lays out who does what, how to communicate, and the phases of responsefrom preparation to recovery. Its not just a document; its a critical part of protecting your business.
What is the NIST 800 171 incident response plan?
ing to NIST SP 800-171 section 3.6, the Incident Response family of security requirements focuses on establishing an operational incident-handling capability for organizational information systems that includes adequate: Preparation. Detection. Analysis.